-
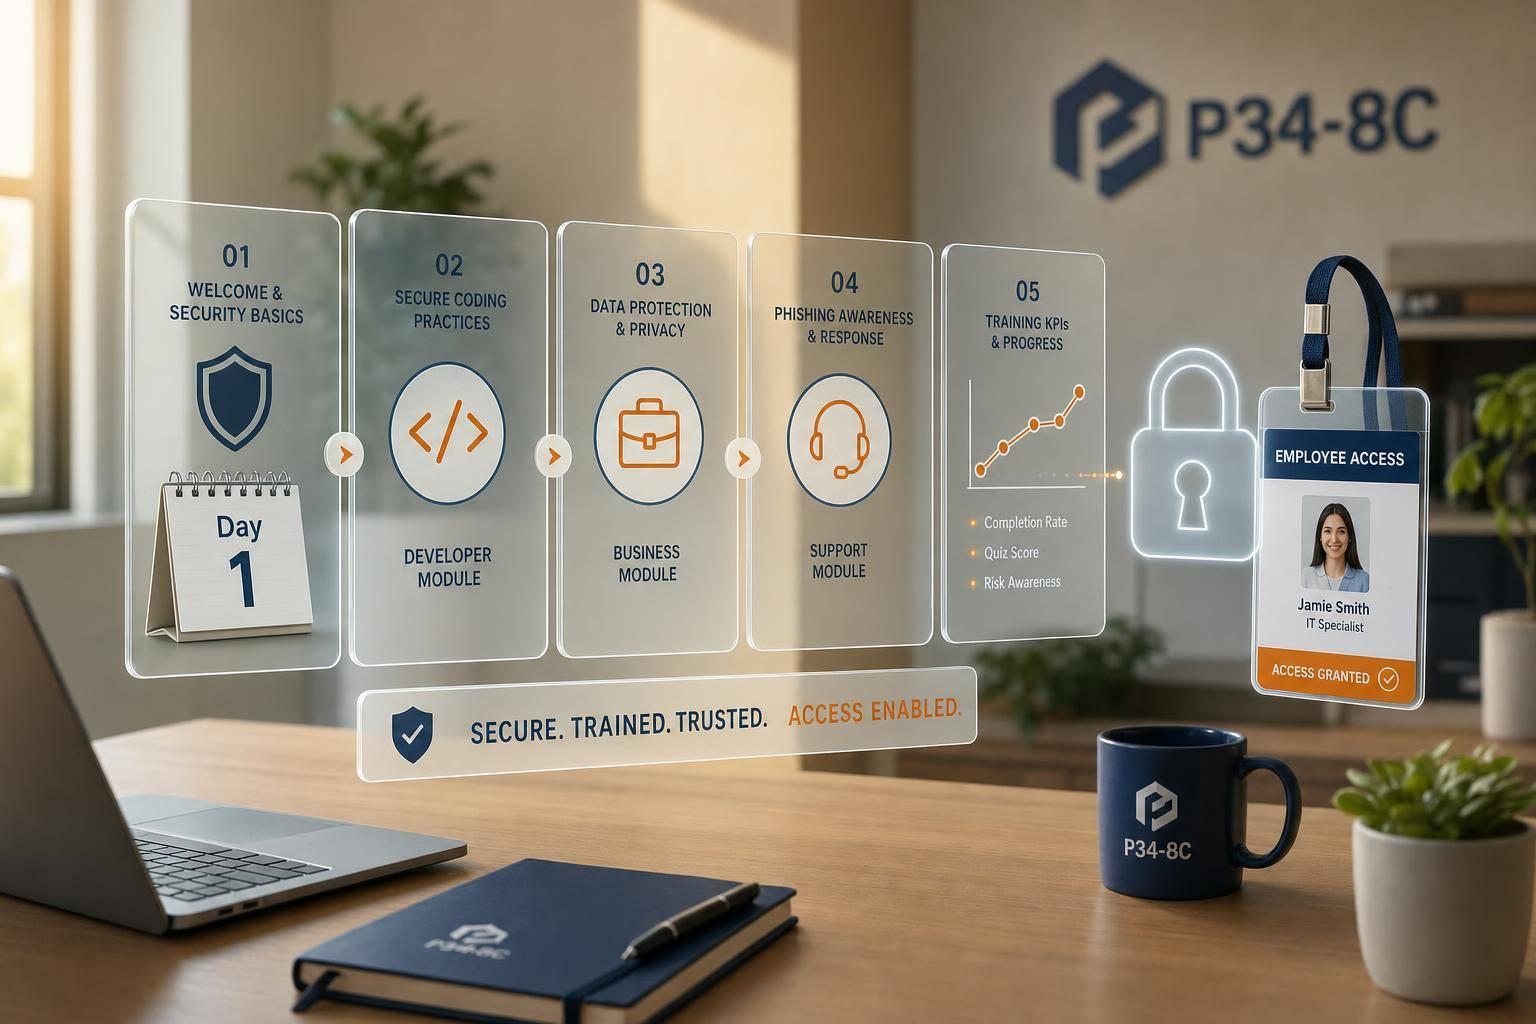
Cybersecurity Training in IT Onboarding
Start security training on day one, tie access to completion, deliver baseline + role-based modules, and track KPIs to reduce risk.
-
Cyber Risk Quantification vs. Qualitative Assessment
Use qualitative scoring for fast prioritization and quantification when dollars matter for budgets, insurance, or board decisions.
-
Hybrid Cloud Integration: Step-by-Step Guide
Four-step hybrid cloud roadmap: inventory apps, secure connectivity and identity, deploy with IaC/CI/CD, then operate with observability, DR, and cost control.
-
How to Integrate Threat Intelligence into IT Workflows
Threat intelligence must change IT decisions: integrate feeds into SIEM/SOAR/ITSM, prioritize exploited CVEs, automate enrichment, and measure MTTD/MTTR.
-
How Much Risk Is Hiding in Your Legacy Software?
Pinpoint security, compliance, and performance risks in legacy systems and learn practical steps—risk assessments, cloud migration, and managed security.
-
How to Modernize a Legacy System Without Breaking It.
Modernize legacy systems without disruption: assess dependencies, apply the 7 R’s, migrate in phases, run parallel stacks, automate tests, and add zero-trust.
-
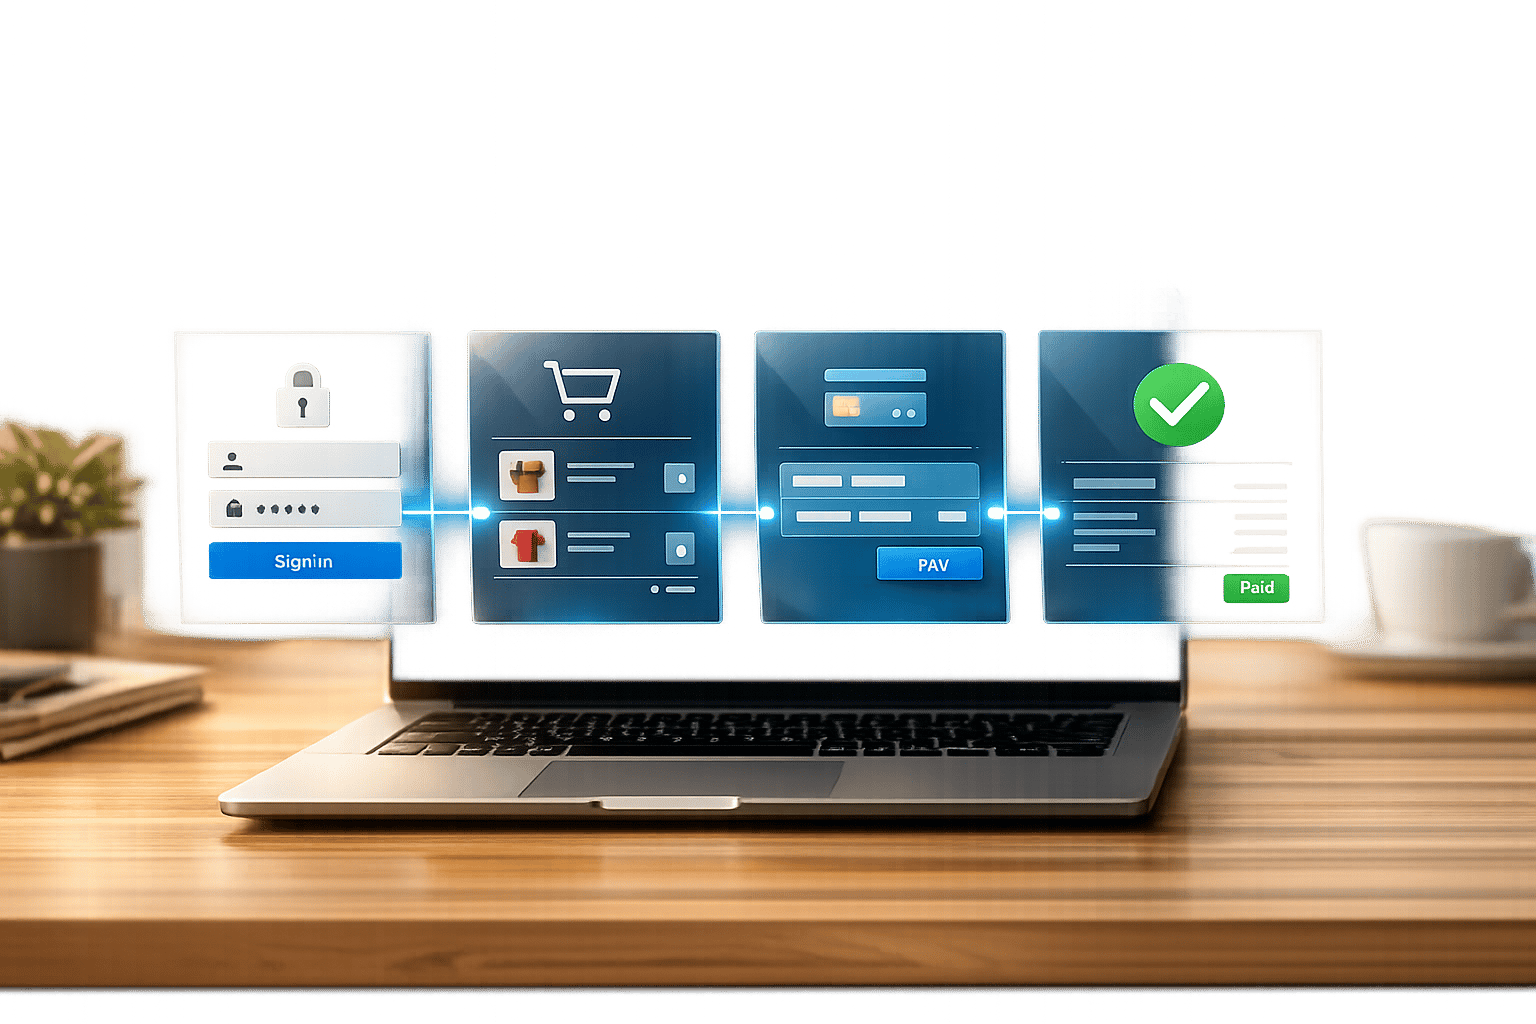
Why You Need End-to-End Tests, not just unit tests.
E2E tests validate full user workflows, catch integration and environment bugs unit tests miss, and protect critical flows like login, checkout, and payments.
-
What QA Automation Actually Buys You.
How QA automation speeds testing, increases coverage, lowers defect costs and scales CI/CD — delivering measurable ROI within months.
-
Why You Need Security Scans in Your Build Pipeline.
Embed SAST, SCA, and container/IaC scans into your CI/CD to catch secrets, vulnerable dependencies, and misconfigurations early for compliance and lower risk.
-
Why Your Software Needs a Supply Chain Security Strategy.
Ignoring software supply chain security invites widespread breaches; adopt SBOMs, NIST SSDF, vendor controls and hardened CI/CD to reduce risk.